Quick Take
You will not fix data management by buying a platform. You fix it by picking the discipline where a failure would cost you most this quarter and putting a real rule behind it: a measurable quality requirement, a minimization habit, a written access policy, a tested recovery plan, or a governance structure that keeps the rest from drifting. Do one properly, then add the next.
Most businesses do not decide to manage data badly. They just never decide to manage it at all. Files pile up in shared drives, a customer list lives in three spreadsheets, and access gets handed out by whoever asks loudest. It works fine until it doesn’t: a bad mailing list, a leaked record, or an outage nobody planned for.
The fix is a set of disciplines that established frameworks already describe, and that any business can adopt at its own pace. This guide covers five: data quality, data security, access control, resilience, and governance. Each comes with a recognized reference you can lean on and a practical way to start.
What Effective Data Management Actually Means
Effective data management is the practice of structuring, governing, and optimizing your data so it stays accurate, protected, available, and aligned with what the business is trying to do. The DAMA Data Management Body of Knowledge (DAMA-DMBOK) frames this as a set of principles, practices, and functions that organizations use to build, scale, and govern data programs, with explicit attention to standardization, compliance, and strategic alignment.
That is the umbrella. Underneath it sit the five pillars this guide walks through:
- Data quality: is the data accurate, complete, and fit for the decision it feeds?
- Data security: are you collecting only what you need, protecting it, and disposing of it safely?
- Access control: who is allowed to see and use which data, and how is that decided?
- Resilience: can you keep operating, or recover quickly, when systems fail?
- Governance: is there a structure that keeps all of the above consistent and tied to business strategy?
Governance is the glue. It is the reason the other four do not drift apart into disconnected projects. Read the pillars in order, but expect to circle back to governance once the operational pieces are in motion.
Pillar 1: Data Quality
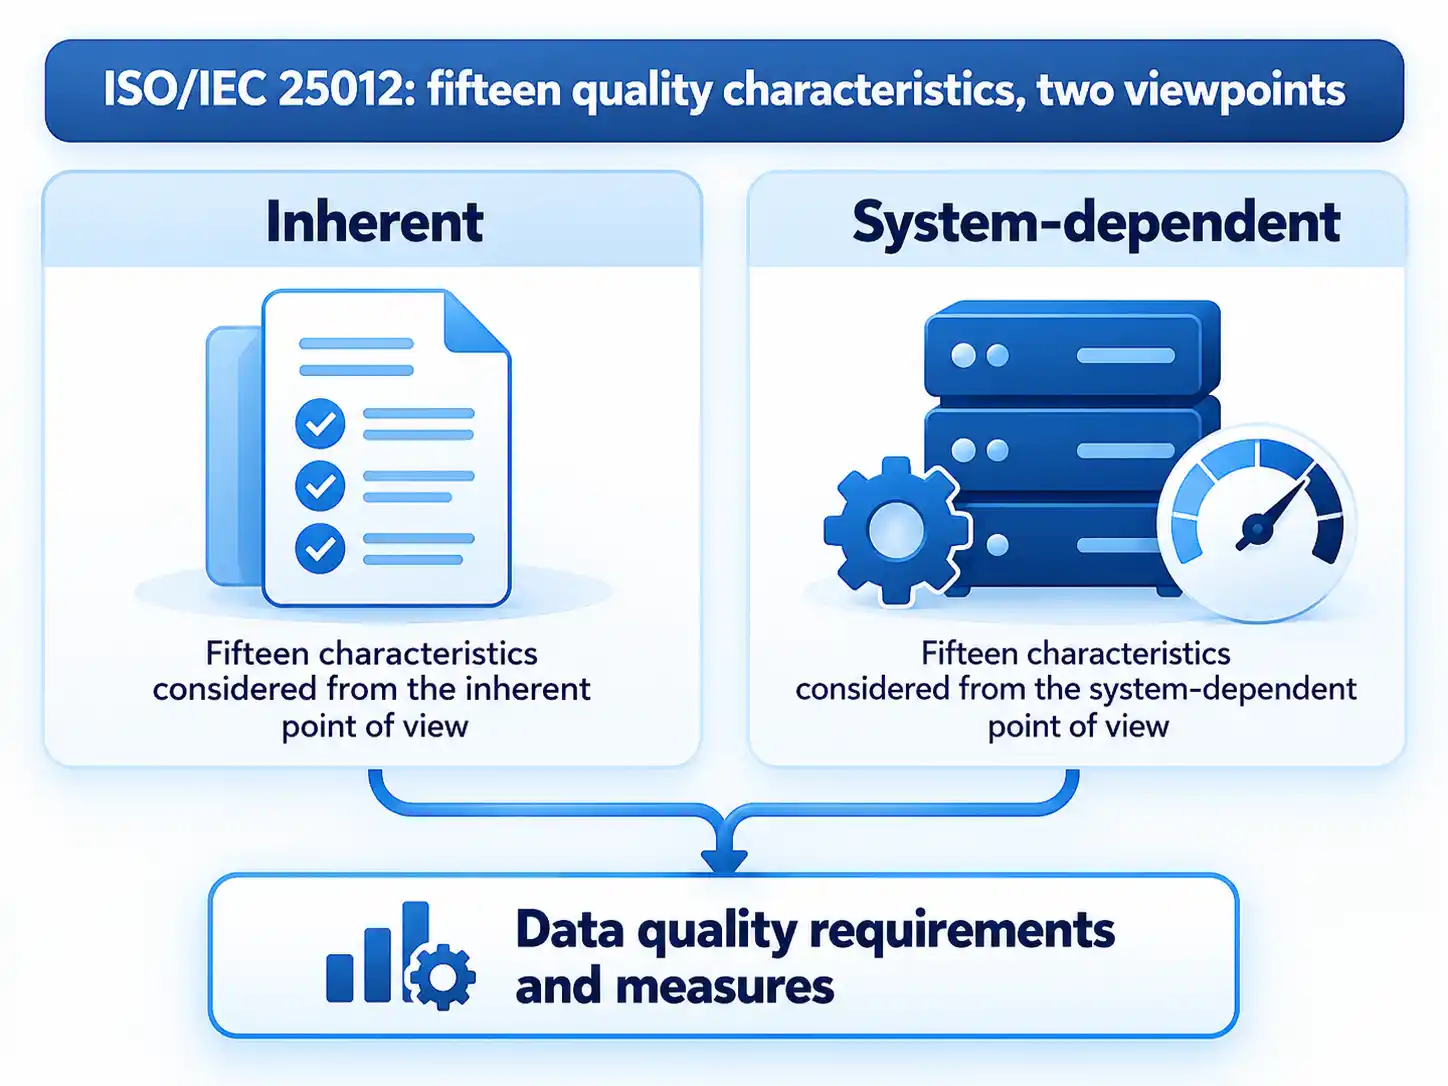
Data quality is where most data problems actually begin, and it is the pillar most businesses skip because “the data looks fine.” The useful starting point is a quality model, not a gut feeling. ISO/IEC 25012:2008 defines a general data quality model for structured data and categorizes quality attributes into fifteen characteristics, viewed from two angles: inherent and system-dependent.
That distinction is the single most under-taught idea in data quality. Inherent characteristics describe the data itself, whether it is accurate, complete, and consistent regardless of where it lives. System-dependent characteristics describe how well the surrounding system supports the data, things like availability and how easily it can be maintained. A record can be perfectly accurate (inherent) and still be unusable because the system serving it is unreliable (system-dependent). Fixing one does not fix the other.
The standard is designed to help you establish data quality requirements, define measures, and plan evaluations. You can use it to define and evaluate requirements in data production and integration, or to check whether data complies with legislation. That is a practical toolkit, not an academic exercise.
How to Set Data Quality Requirements
Use the ISO/IEC 25012 model to turn vague complaints about “bad data” into requirements you can measure and check.
- Define the requirement in business terms. Pick one dataset that matters, such as a customer list, a product catalog, or a billing table, and state what “good” means for the decision it supports. Write it as a plain sentence before touching any tool.
- Choose the relevant characteristics. From the fifteen characteristics, select only those that matter for this dataset. The standard notes that characteristics carry different importance and priority for different stakeholders, so do not try to optimize all of them at once.
- Separate inherent from system-dependent concerns. For each chosen characteristic, note whether it is about the data itself or about the system serving it. This tells you whether to fix the record or fix the platform.
- Define measures and evaluate. Set a concrete measure for each requirement, then plan and perform an evaluation against it. The standard is explicitly built to support defining measures and running evaluations, including checking compliance with legislation or requirements.
Verify the result
- Every quality requirement is written as a measurable statement, not an opinion.
- Each requirement is tagged as inherent or system-dependent so the fix has a clear owner.
- You have run at least one evaluation and recorded the result against the measure.
Pillar 2: Data Security
Data security is often treated as an IT problem. The Federal Trade Commission’s data security guidance frames it differently: as a legal obligation that starts with a decision about what data you collect in the first place. The FTC’s core advice is a three-part cycle: collect only what you need, keep it safe, and dispose of it securely.
That guidance is not written only for large enterprises. The FTC publishes free resources for businesses of any size, including its Safeguards Rule guidance and the “Start with Security” guide for business, aimed at ordinary companies handling sensitive customer or employee information.
Warning
Data security is a legal obligation, not just a technical preference. As the FTC explains, a sound security plan to collect only what you need, keep it safe, and dispose of it securely helps you meet your legal duty to protect sensitive personal information. Treat data minimization as a governance decision, not a default setting.
The practical upshot: before you harden anything, ask what you are storing and why. Every record you never collect is a record you cannot leak. That single discipline does more for most small businesses than any security product.
Pillar 3: Access Control
Access control is the discipline of deciding who gets in. NIST defines access control as the process of granting or denying specific requests to obtain and use information and related processing services, and to enter specific physical facilities. That definition is broader than most people expect, since it covers digital data and physical entry alike.
In practice, access control is a policy question before it is a technology question. Most access problems come from a missing rule, not a missing tool: someone was granted access for a project and never had it removed, or a shared login means nobody can be held accountable.
How to Build a Grant/Deny Access Policy
Turn the NIST definition into a simple written policy that answers “who can access what, and how do we decide?”
- Inventory what needs protecting. List the systems, datasets, and physical spaces that hold sensitive information. Group them by sensitivity so you are not writing a separate rule for every file.
- Define roles, not individuals. Assign access to job roles rather than named people. This keeps the policy stable when staff change and makes it obvious when someone’s access should be revoked.
- Write the grant/deny rule. For each role and resource, state clearly whether access is granted or denied by default. A default-deny posture is the safer starting point.
- Set a review cadence. Schedule a periodic review so access granted for a project gets removed when the project ends. Document who approves exceptions.
Verify the result
- Every sensitive resource is mapped to at least one role.
- No shared logins remain for sensitive systems.
- A named person owns the review, and the next review date is on the calendar.
Pillar 4: Resilience and Contingency Planning
Resilience is what keeps a bad day from becoming a lost quarter. NIST SP 800-34 Rev. 1 is a contingency planning guide that explains the purpose, process, and format of information system contingency planning through practical, real-world guidelines. It also covers how contingency planning relates to other security and emergency plans, organizational resiliency, and the system development life cycle.
One limitation to keep in view: this guide is written for federal information systems. Private firms are not bound by it, but the process and templates are adaptable, and that is how most businesses should treat it, as a well-structured model rather than a mandate.
Prerequisites
- A list of your critical systems and the business functions they support.
- Agreement on which functions are most important, so you can prioritize planning effort.
- Awareness that the NIST templates are guidance written for federal systems and should be adapted, not adopted wholesale.
How to Plan for Contingency
Follow the NIST sequence: assess impact, assign an impact tier, then pick the matching template.
- Run a business impact analysis. Use the NIST Business Impact Analysis template to evaluate your systems and operations and determine contingency planning requirements and priorities.
- Assign an impact tier. Classify each system as low, moderate, or high impact based on what happens if it goes down. NIST provides separate templates for each tier.
- Select and adapt the template. Pull the low, moderate, or high impact contingency planning template that matches your tier, then tailor it to your business rather than filling it in verbatim.
- Test the plan. A plan that has never been exercised is a document, not a capability. Run a tabletop exercise and record what breaks.
If you want to go deeper on the monitoring side of resilience, our guide to AI-driven monitoring covers how continuous visibility supports faster detection and recovery.
Pillar 5: Governance and Framework
Governance is the pillar that makes the other four stick. The DAMA-DMBOK is a recognized framework that gives organizations the principles, practices, and functions to build, scale, and govern data programs. Its second edition adds coverage of data ethics, data governance, data integration, and emerging technologies.
What governance buys you, concretely: a common language so teams stop arguing about definitions, guidance on security, privacy, and regulatory adherence, and a way to tie data management to business objectives so data is treated as a strategic asset rather than an IT chore. It also outlines the functions, roles, and methodologies that keep data maintained and usable.
This is where tooling starts to matter, but only after the rules exist. A data catalog software platform can help a growing organization track what data it holds and who owns it, which supports governance. The catalog does not create the governance; it records and enforces decisions you have already made.
Putting It Together
You do not need all five pillars at full strength on day one. You need the right emphasis for your stage. The table below maps business maturity to where to focus first.
| Business stage | Primary focus | Supporting focus | Defer for now |
|---|---|---|---|
| Small business | Data security (minimize, secure, dispose) | Simple access-control policy | Formal quality model, full governance framework |
| Growing / mid-size firm | Data quality (ISO/IEC 25012 model) | Resilience (NIST contingency templates) | Enterprise-wide governance alignment |
| Data-mature organization | Governance (DAMA-DMBOK alignment) | All four operational pillars in parallel | — |
Decision rule: If a failure in a pillar would cause legal exposure or lost revenue this quarter, that pillar goes first. For most small businesses that is security. For a firm whose decisions depend on accurate reporting, it is quality. For an organization already handling data at scale, it is governance, because that is what keeps the rest consistent.
Key Takeaways
- Treat data management as five interlocking disciplines, not a single purchase.
- Anchor quality in the ISO/IEC 25012 model and separate inherent from system-dependent concerns.
- Follow the FTC’s collect-only-what-you-need, keep-it-safe, dispose-securely cycle to meet your legal obligations.
- Write an access-control policy with default-deny and a review cadence.
- Adapt NIST contingency templates to your impact tier, then test the plan.
- Let governance tie the other four pillars to business strategy.
The Bottom Line
Effective data management is unglamorous and cumulative. The businesses that get it right are not the ones that bought the biggest platform. They are the ones that wrote down what “good data” means, decided what they actually need to collect, controlled who could reach it, planned for the day something breaks, and put a structure in place to keep all of that consistent. Pick the pillar where a failure would hurt most this quarter, apply the framework behind it, and build outward from there.
💬 Comments