The most important online casino technology trends in 2026 are the integration of regulation, identity verification, payments, behavioral monitoring, mobile security, cloud infrastructure, and independent testing into a single operating platform. AI, blockchain, crypto, and virtual reality remain relevant technologies, but they are not reliable measures of platform maturity by themselves.
The practical shift is from isolated features to connected systems. A deposit, for example, may depend on identity status, account limits, fraud controls, payment authorization, and account-risk rules before the money can be used for gambling.
Quick Take: The Six Trends That Actually Matter
- Regulation is becoming software behavior.
Rules increasingly affect account states, user-interface choices, financial limits, security controls, and testing procedures. - Identity and payments are converging.
Verification is becoming part of the account lifecycle rather than something postponed until withdrawal. - Behavioral monitoring is becoming more automated.
Operators in regulated markets may need systems capable of combining account, spending, time, and behavioral indicators quickly enough to act on risk. - Cloud maturity is about control.
Hosting location matters less than whether operators can maintain security, auditability, resilience, and oversight across service providers. - Mobile security is its own engineering problem.
Authentication, local data storage, network communication, device integrity, and app tampering all require dedicated controls. - Testing increasingly covers the whole platform.
Game fairness remains important, but certification can also involve accounts, payments, live gaming, cloud services, security, and third-party systems.
1. Regulation Is Becoming Software Behavior
The simplest way to understand this trend is that regulation no longer lives only in licence applications and policy documents. In mature regulated markets, some rules must be translated directly into software behavior.
Great Britain’s remote technical standards, for example, cover customer account information, transaction displays, random outcomes, interrupted gambling, financial limits, responsible product design, live dealer studios, and security requirements. That means compliance can influence the database, user interface, business rules, testing process, and deployment workflow rather than being handled by a legal team alone.
Financial limits show how concrete this can become. Current rules already require accessible facilities for customers to apply limits. Additional UK Remote Gambling and Software Technical Standards requirements scheduled for September 30, 2026 will clarify gross deposit limits and require the gambling system to stop further deposits when the applicable deposit limit has been reached until the defined period restarts or the permitted increase process is completed. These are upcoming RTS changes, not requirements already in force on September 7, 2026.
For practitioners, this creates a version-control problem as much as a regulatory one. A compliant rule can be broken by a redesigned cashier screen, an incorrectly configured jurisdiction, a wallet migration, or a third-party integration that does not honor the same account state.
The important limitation is jurisdiction. A design mandated in Great Britain cannot automatically be described as a global casino requirement.
2. Identity, Account State, and Payments Are Converging
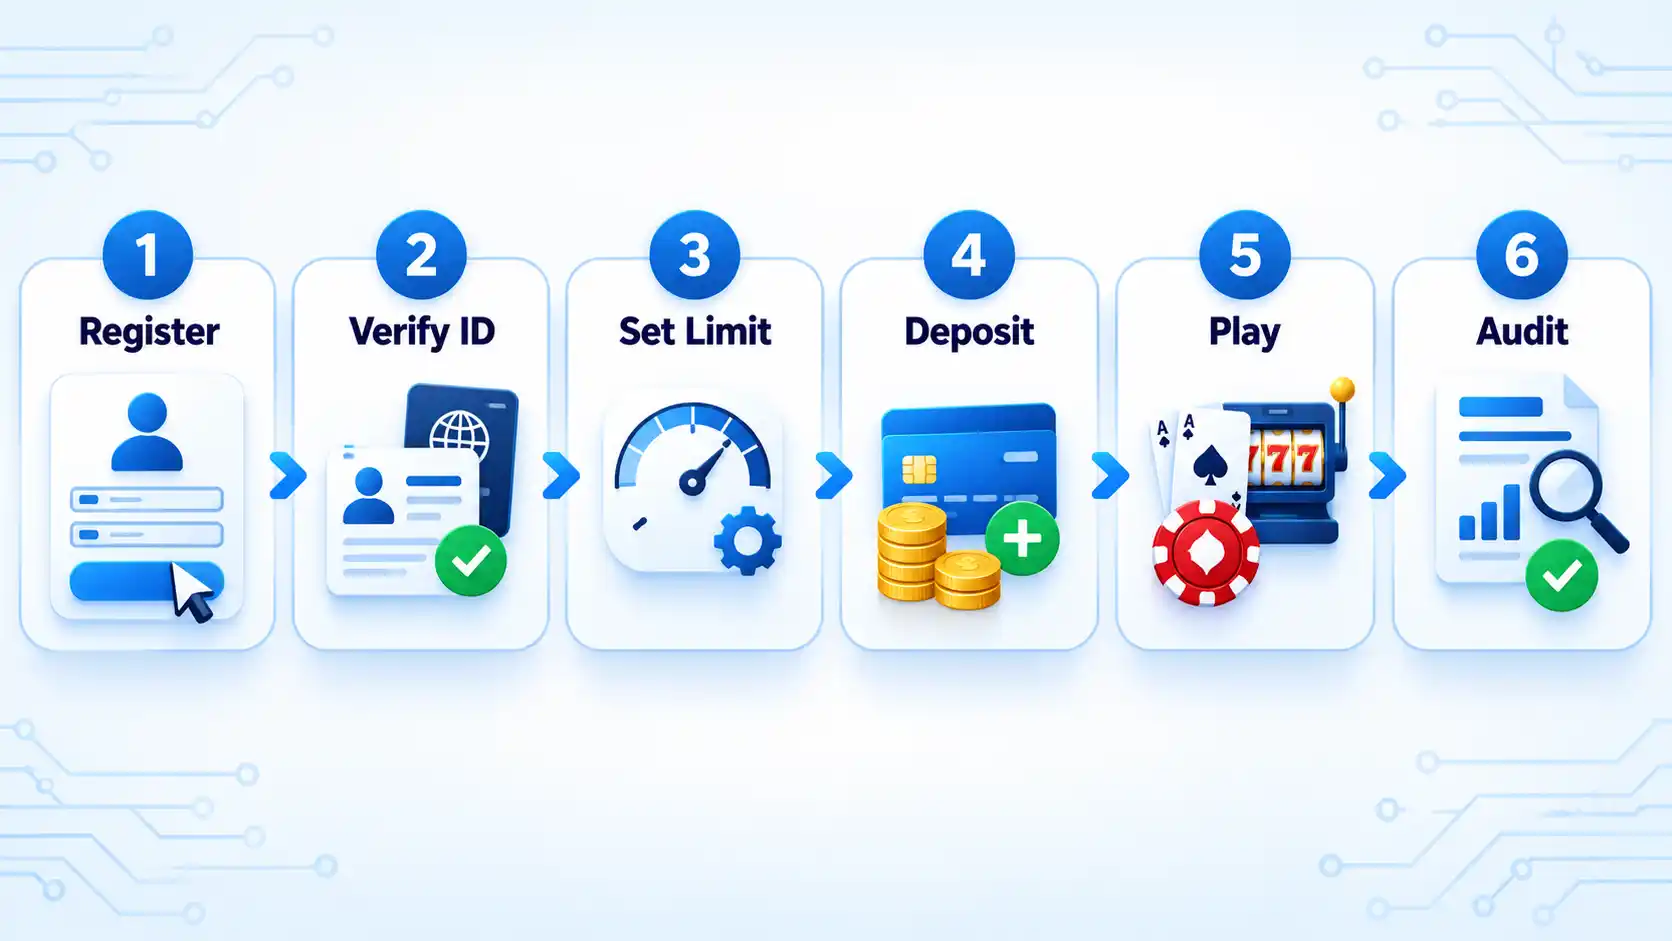
Identity verification is moving closer to the beginning of the account journey. Know Your Customer, commonly shortened to KYC, describes processes used to establish and verify who a customer is. The exact legal requirements vary by country, but technically the result becomes an account state that other systems need to understand.
A recent UK Gambling Commission reminder states that remote operators must establish identity before permitting a customer to gamble and, at minimum, provide assurance that the customer’s name, address, and date of birth belong to the same person. It also says a withdrawal request should not trigger additional information requirements when that information could reasonably have been requested earlier. The Commission’s August 2026 identity verification guidance makes the connection between verification timing and the customer journey especially clear.
Technically, this pushes identity away from being a standalone document-upload form. A modern account may pass through states such as registered, identity pending, identity verified, deposit eligible, withdrawal restricted, limit reached, or manually reviewed. Payment and gaming services then need consistent answers about which actions are allowed.
That consistency matters when evaluating an online casino. The visible cashier or registration page is only one layer. Behind it may be separate identity, fraud, wallet, payment, and account-management services.
A common failure point is state mismatch. An identity provider may report that verification is complete while the wallet service still treats the account as unverified. The result can be repeated document requests, rejected payments, or unnecessary withdrawal friction even when each service works correctly in isolation.
3. Behavioral Monitoring Is Becoming a Real-Time Data System
Modern account monitoring is increasingly a data-engineering problem. Instead of evaluating one transaction by itself, a platform can combine signals from several parts of the customer’s account history.
UK Gambling Commission guidance requires remote licensees to maintain systems and processes that monitor customer activity for indicators including customer spend, patterns of spend, time spent gambling, behavioral indicators, customer contact, use of gambling-management tools, and account indicators. Its customer interaction guidance also makes clear that the purpose is to identify relevant risk without simply waiting for a long behavioral pattern to emerge.
In engineering terms, the flow can look like this: account events are collected, relevant indicators are calculated, rules or models evaluate those indicators, an action is selected, and the result is logged for later review. An action might involve an automated control, a message, or escalation to staff depending on the rules and circumstances.
This is where terminology needs discipline. Automation is not automatically artificial intelligence. A threshold such as “flag account when conditions A, B, and C occur” is automated logic even if no machine-learning model is involved. Some platforms may use predictive models or AI for fraud analysis, classification, or personalization, but that capability should not be confused with a regulatory requirement to use AI.
The main technical challenges are data quality and timing. A monitoring system can produce poor results if payment data arrives late, multiple brands maintain separate account histories, limit changes are stored in another service, or the same customer is represented by inconsistent identifiers.
Practitioners also have to consider false positives and model or rule drift. A system that flags too many normal accounts creates unnecessary review workload. A system that rarely flags anything may fail for the opposite reason. Readers unfamiliar with how data is combined and interpreted can use our beginner’s guide to data analytics for the underlying concepts.
4. Cloud Architecture Is Now About Control, Not Novelty
Using cloud infrastructure is no longer a meaningful technology trend by itself. The more useful question is whether the operator can maintain control and evidence across an increasingly distributed collection of services.
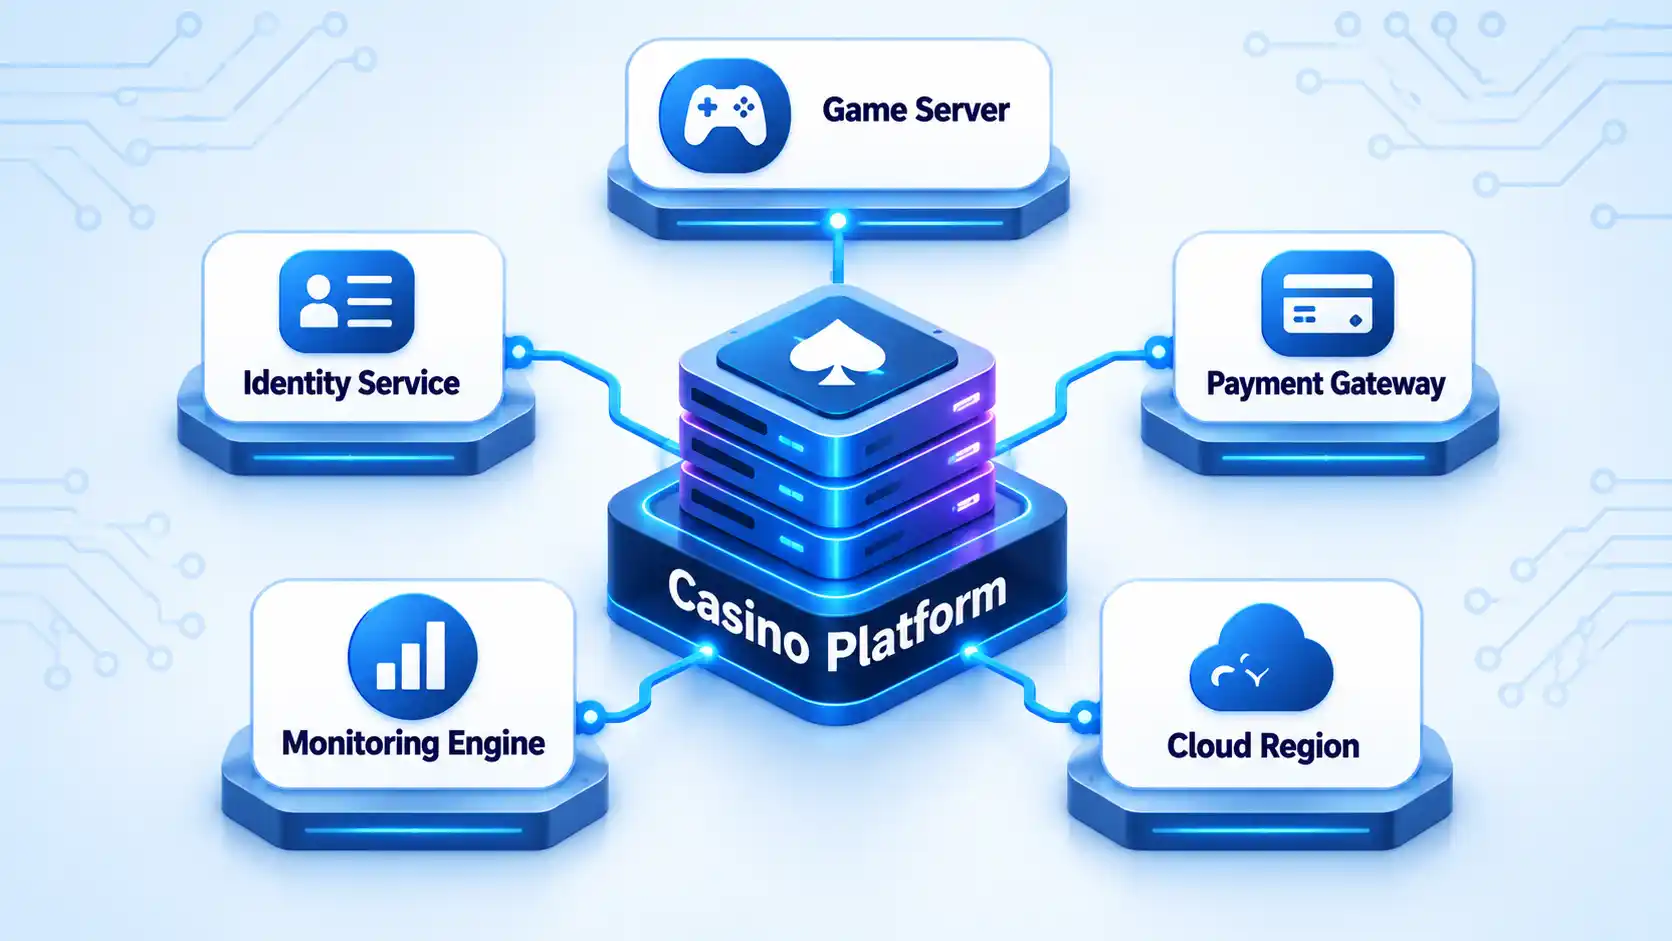
An online casino may depend on a game platform, identity provider, payment gateway, fraud service, analytics pipeline, content-delivery network, customer-support platform, and several game suppliers. Some components may run in different cloud regions or be operated entirely by another company.
That architecture can improve scalability and resilience, but it also creates dependencies. If the identity service becomes unavailable, new registrations may fail even though the casino website is still online. If a logging service loses events, an operator may have an audit gap despite the game servers continuing normally.
For practitioners, the important controls include:
- which supplier can access regulated or sensitive data;
- where critical data is stored and replicated;
- how administrative access is authenticated and logged;
- how failures are detected and recovered;
- which party owns each operational control;
- how software and configuration changes are reviewed; and
- whether evidence remains available for auditors and regulators.
The UK Gambling Commission’s security requirements are now based on relevant sections of ISO/IEC 27001:2022 and are intended to reduce unnecessary security risk to remote-gambling customers. The regulator describes these security requirements as part of the technical compliance baseline rather than an optional cloud feature.
A multi-region deployment therefore is not automatically more mature than a simpler architecture. Redundancy helps only if data consistency, access control, recovery procedures, and regulatory obligations remain manageable.
5. Payments and Mobile Apps Have Their Own Security Boundaries
Casino platforms process financial and identity data through systems that frequently extend beyond the game itself. Payment-card environments, for example, may fall within the Payment Card Industry Data Security Standard when they store, process, transmit, or otherwise affect cardholder-data environments.
The current PCI Security Standards Council document library lists PCI DSS v4.0.1 as the active version. PCI DSS is not a gambling-specific certification, but it provides a useful security baseline for payment-card environments.
Mobile applications add another boundary because the operator does not control the customer’s device. Sensitive information can be exposed through insecure local storage, weak authentication, unprotected network traffic, unsafe interaction with the operating system, outdated code, or insufficient resistance to tampering.
The OWASP MASVS framework separates mobile security into categories covering storage, cryptography, authentication and authorization, network communication, platform interaction, code quality, resilience, and privacy. It is useful for understanding the mobile attack surface, but it should not be described as proof that a casino app has passed gambling-specific certification.
One practical example is session handling. A password can be protected correctly while an application still mishandles the token that keeps the user logged in. Protecting authentication credentials therefore does not eliminate the need to protect session data, network calls, and device-side state.
This is also why payment security should not be reduced to a claim such as “uses encryption.” The relevant question is which systems handle sensitive data, where trust boundaries sit, and what happens when one component is compromised or unavailable.
6. Independent Testing Is Becoming a Platform Trust Layer
Casino testing is often simplified to the Random Number Generator, or RNG, which produces outcomes for relevant games. RNG testing remains important, but interactive-gaming assurance can extend much further.
Gaming Laboratories International currently lists GLI-19 v3.0 for interactive gaming systems. Its scope includes areas such as player-account management, random outcome generation, game fairness, interrupted games, live gaming, technical security, data integrity, third-party providers, cloud services, and payment services.
This matters because a casino is usually an ecosystem rather than a single application. A consumer-facing lobby may present games from many suppliers through one account and wallet. Products such as Betway Casino illustrate the familiar single-lobby presentation, but the front-end catalog alone cannot tell a reader how individual suppliers, versions, or backend services were tested.
For practitioners, certification creates a change-management problem. A system can be tested in one configuration and then change. A new game build, wallet component, server configuration, integration, or supplier version may need evaluation according to the applicable jurisdiction and certification process.
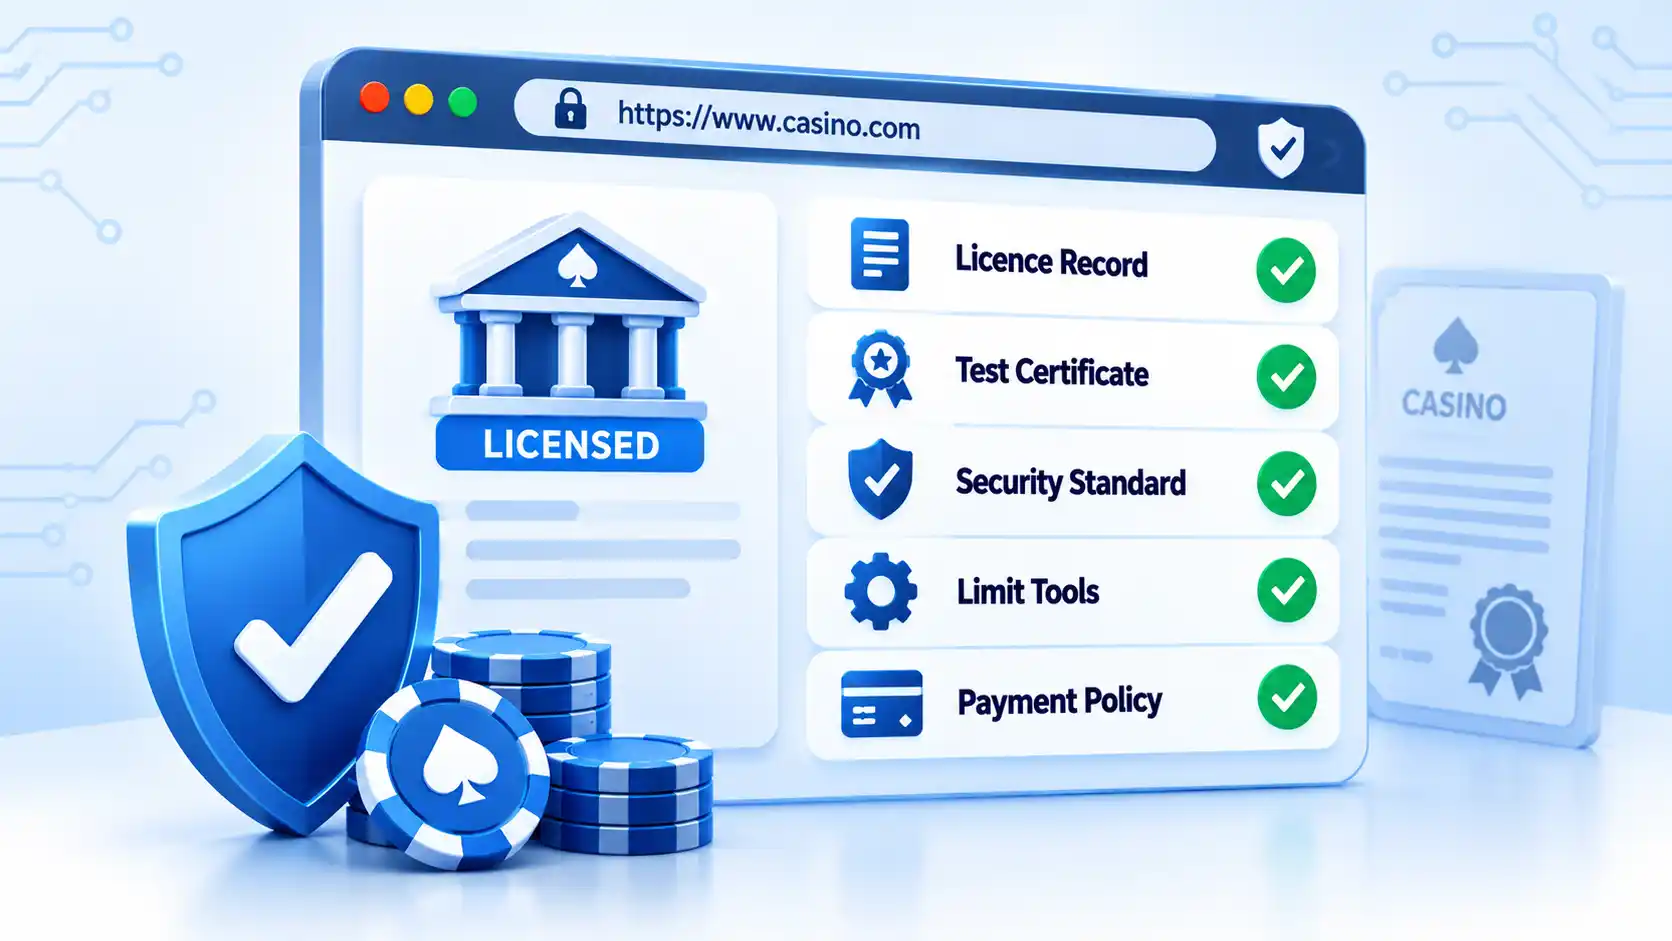
This is why a generic “certified” badge is weak evidence without context. Useful evidence identifies the testing body, product or system, version or scope, and relevant jurisdiction where that information is available.
GLI-19 itself is a technical standard and certification reference, not a law that automatically applies everywhere. The governing regulator and licence conditions determine which evidence is legally required.
How the Trends Fit Together
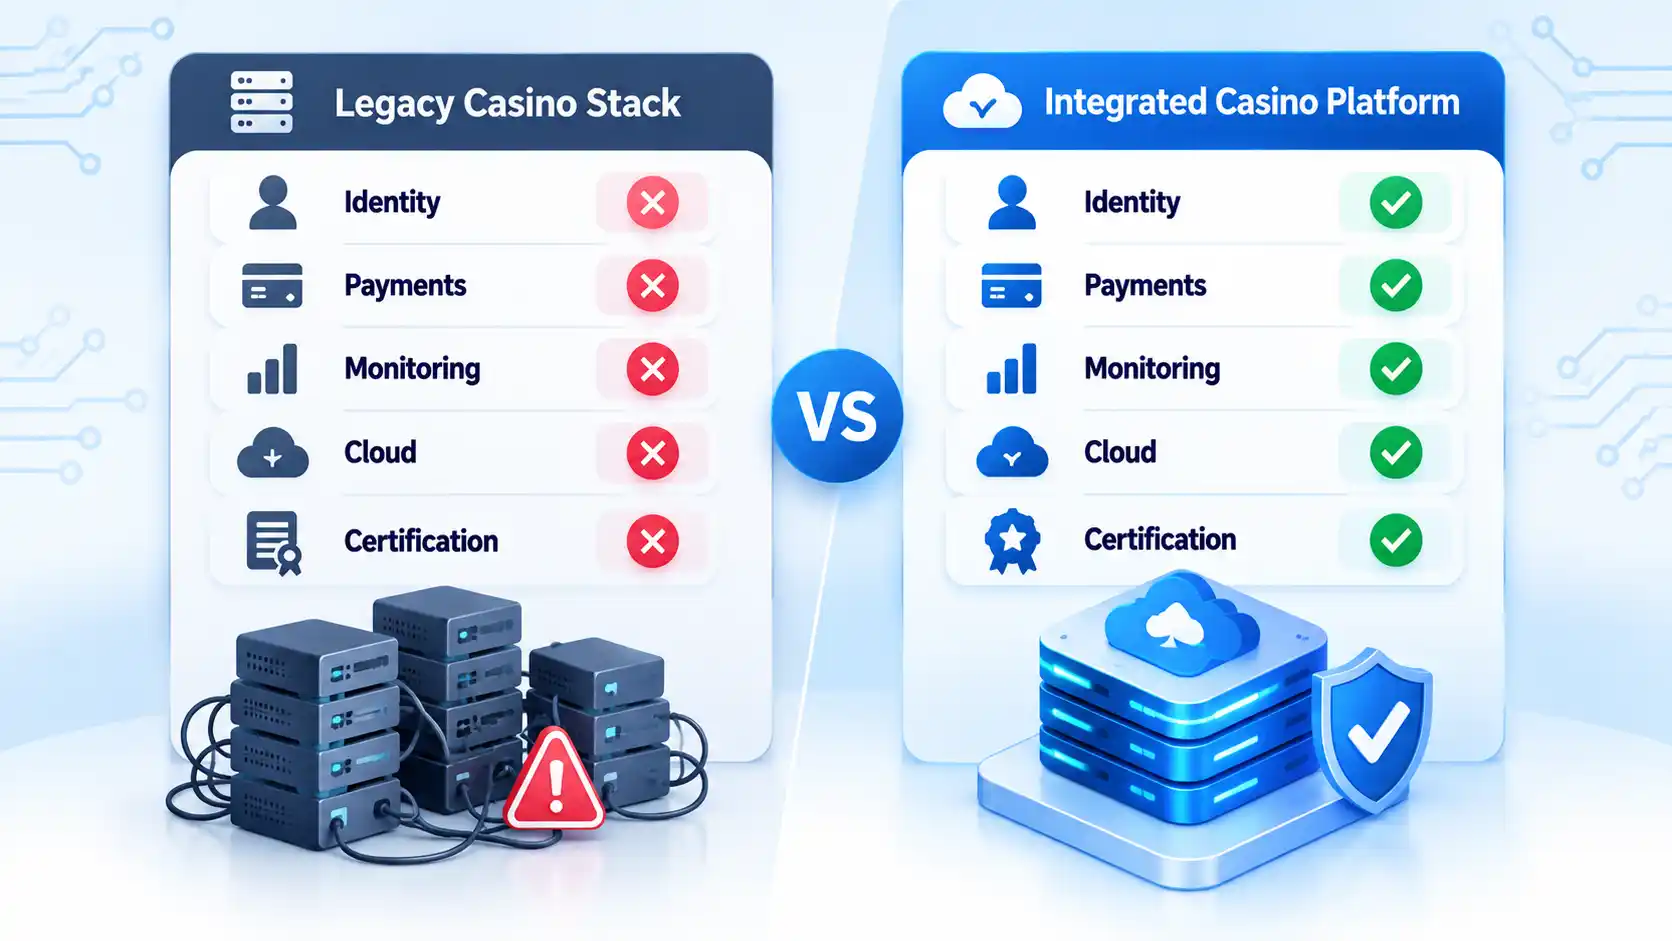
The common pattern is not a particular programming language, cloud provider, or AI model. It is the need to keep account state consistent across systems while preserving enough evidence to explain what happened. The table below shows what each trend changes and where the main failure points appear.
| Trend | Technical change | Operational value | Typical failure mode | Useful evidence |
|---|---|---|---|---|
| Regulation in software | Rules become enforceable account and interface states | More consistent rule execution | Jurisdiction or product rules implemented incorrectly | Regulator standards and test records |
| Integrated identity | Verification status connects to account actions | Checks occur earlier in the lifecycle | Conflicting states between vendors | Licence requirements and documented workflow |
| Behavioral monitoring | Account signals feed automated decision processes | Faster identification and action | Missing data, delay, or false positives | Monitoring controls and audit records |
| Cloud services | Critical functions span several providers or regions | Scalability and resilience options | Vendor outage or incomplete audit visibility | Architecture, access, and recovery evidence |
| Mobile security | Controls extend onto an untrusted user device | Protection for app sessions and sensitive data | Authentication, storage, network, or tampering flaws | Security assessment scope |
| Platform certification | Testing covers multiple system components | More structured supplier assurance | Version or configuration drift | Traceable test or certification records |
The trade-off is complexity. Connecting more services can improve control and automation, but every additional dependency creates another interface where data can arrive late, permissions can be misconfigured, or responsibility can become unclear.
What About AI, Blockchain, VR, and Crypto?
These technologies should be treated as capabilities rather than automatic signs of progress.
Artificial intelligence
AI can support fraud classification, behavioral analysis, personalization, document processing, or customer-service systems. The important questions are what data feeds the model, what decision it influences, how errors are handled, and whether important actions remain explainable and reviewable. An automated monitoring requirement does not automatically require machine learning.
Blockchain
Blockchain can change how transactions or certain game records are stored and verified. It does not remove the need to assess the operator, application security, wallet or key management, identity requirements, or dispute process.
Virtual and augmented reality
Virtual reality and augmented reality can create new interfaces, but interface novelty is different from platform maturity. Without stronger evidence of mainstream adoption, they are better treated as specialized presentation technologies than as foundational 2026 infrastructure trends.
Cryptocurrency
Crypto can provide an alternative payment rail where law and operator policy allow it. It also introduces different wallet, custody, transaction-monitoring, volatility, and regulatory considerations. Its presence does not make a platform inherently more advanced or secure.
How to Judge Whether the Technology Is Mature
You do not need access to the source code to distinguish meaningful technical evidence from marketing language. Look for claims that can be tied to a regulator, standard, test scope, or documented process.
Checklist
- Verify the licence rather than the logo.
Check the operator and domain against the relevant regulator’s public information where available. A detailed verification workflow belongs in our planned online casino licence verification guide. - Check when identity verification happens.
Repeated surprise checks at withdrawal can indicate a poorly coordinated account process, although some later checks may still be legally or operationally necessary. - Read financial-limit controls.
Look at how limits are defined, changed, confirmed, and enforced rather than assuming the presence of a “responsible gambling” page proves implementation quality. - Look for named security or testing standards.
“Secure” or “certified” means little without the scope, testing body, standard, or version. - Check error handling.
Mature platforms explain interrupted games, failed deposits, pending verification, and unavailable services rather than leaving the account in an ambiguous state. - Separate platform security from personal security.
Passwords, phishing, two-factor authentication, and device protection deserve their own treatment in our planned online casino security guide. - Separate payment architecture from payment-method choice.
Deposit methods, withdrawal processing, e-wallets, cards, and other rails are covered more usefully in a dedicated online casino payments guide.
Key Takeaways
- The strongest 2026 casino technology trend is integration: regulation, identity, payments, monitoring, security, and testing increasingly depend on the same account state.
- Regulation can influence software behavior directly, including interface design, transaction rules, security controls, and testing.
- Automated monitoring is a verifiable trend, but it should not automatically be described as AI.
- Cloud maturity depends on access control, auditability, supplier governance, data integrity, and recovery rather than simply using cloud infrastructure.
- Mobile apps add security requirements around authentication, local storage, network communication, platform interaction, and tamper resistance.
- Independent assurance is stronger when the testing body, scope, system version, and jurisdiction can be identified.
FAQ
Do online casino games run on the casino’s own servers?
Not necessarily. An operator can integrate games or services supplied and hosted by third parties while presenting them through one account and lobby. The architecture varies by operator and supplier. This is why responsibility for third-party access, monitoring, outages, testing, and data flows matters.
Can an online casino change a game after it has been certified?
Software can be updated, but a material change may trigger testing, approval, or documentation requirements depending on the jurisdiction and certification framework. A certificate should therefore be understood in relation to a particular product, version, configuration, or test scope rather than as permanent approval of every future build.
Why can the same casino account behave differently on the app and website?
The app and website may share the same backend account while using different session handling, device permissions, interface code, cached data, and release versions. A backend account can therefore be healthy while one client has a login, display, or compatibility problem.
Does using a cloud provider make an online casino more secure?
No. A cloud provider can supply strong infrastructure controls, but the operator and its vendors still have to configure access, identities, logging, networks, software, backups, and data handling correctly. Cloud infrastructure changes the responsibility model; it does not remove security responsibility.
Is AI required for responsible-gambling monitoring?
Not as a general rule. Regulators can require monitoring, timely identification, and automated actions without specifying machine learning. A platform can satisfy an automation requirement with rules, thresholds, statistical systems, or other mechanisms where those approaches meet the applicable regulatory requirements.

💬 Comments