External penetration testing starts outside an organization’s trusted network and asks what an internet-based attacker could reach, while internal penetration testing starts from an assumed or provided foothold inside the environment and asks how far that access could extend. Neither approach is universally better because each answers a different security question.
What Network Penetration Testing Actually Tests
A penetration test does more than list vulnerable software versions or open ports. The U.S. National Institute of Standards and Technology (NIST) describes penetration testing as a security assessment technique that mimics real-world attacks and can show how weaknesses may be combined to gain greater access. Its Technical Guide to Information Security Testing and Assessment also distinguishes vulnerability identification from the controlled validation performed during a penetration test.
That distinction matters because a vulnerability scanner can identify hosts, services, configurations, and suspected weaknesses without proving that those findings form a practical attack path. Penetration testing adds controlled validation within an agreed scope so the organization can understand what an identified weakness could actually expose.
Effective penetration testing therefore goes beyond identifying a possible weakness and examines what an authorized tester can demonstrate within defined boundaries.
The practical difference between penetration testing and vulnerability scanning is whether the assessment only identifies likely weaknesses or also validates meaningful attack paths within its authorized scope.
Internal vs External Penetration Testing at a Glance
The most important difference is the tester’s starting position. External testing examines the environment from outside the security perimeter. Internal testing begins from within the environment with a defined level of access and investigates whether that access can be expanded.
| Feature | External Penetration Testing | Internal Penetration Testing |
|---|---|---|
| Starting position | Outside the trusted network, normally with limited target information | Inside the environment with an agreed foothold or level of access |
| Primary question | What can an outside attacker discover, reach, and exploit? | What could happen after internal access has already been obtained? |
| Typical target surface | Internet-facing hosts, remote-access services, public network services, gateways, and other exposed assets within scope | Internal hosts, identity systems, access controls, trust relationships, network services, and network segments within scope |
| Initial access | No trusted internal foothold is assumed | A defined internal foothold or network position is provided or assumed |
| Typical security focus | Internet exposure, perimeter weaknesses, externally reachable services, and initial compromise paths | Privilege escalation, excessive access, internal exposure, segmentation weaknesses, and reachable systems after compromise |
| What the result demonstrates | How exposed the organization is to attacks beginning outside its trusted environment | How effectively internal controls restrict the consequences of an existing foothold |
These are starting perspectives rather than rigid limits on every later action. NIST explains that an external tester who compromises a reachable host may, when the agreed scope allows it, use that access to investigate hosts that are not normally accessible from outside the network. An external engagement therefore does not automatically end when the first perimeter system is compromised.
How External Network Penetration Testing Works
External network penetration testing approaches the environment from an outsider’s perspective. In NIST’s description of an outsider scenario, the tester has little or no specific knowledge of the target beyond information such as authorized IP addresses or address ranges.
The assessment normally begins by identifying the authorized internet-facing attack surface. Depending on scope, this may include public IP addresses, externally reachable network services, remote-access infrastructure, mail services, DNS-related infrastructure, firewalls, gateways, and other systems exposed through public networks.
Discovery establishes what is visible and reachable. The tester can then analyze suspected weaknesses and, where the Rules of Engagement permit it, validate selected findings in a controlled manner. The useful question is not simply how many potential vulnerabilities exist, but whether those weaknesses create a meaningful route to systems, privileges, or data the organization intended to protect.
Perimeter technology also affects what can be reached from outside. For example, a firewall and an SD-WAN platform perform different network functions, so deploying one technology does not by itself establish that every internet-facing path is adequately controlled.
If an external test obtains an initial foothold, the next action depends on scope. One engagement may stop after proving the initial compromise, while another may permit limited post-compromise validation to determine what that foothold exposes. Those boundaries should be agreed before testing begins.
How Internal Network Penetration Testing Works
Internal penetration testing starts on the other side of the perimeter. NIST describes an internal test as one in which testers are on the internal network and have been granted some level of access to the network or specific systems.
The starting position might represent a compromised employee account, a workstation connected to an internal segment, a low-privilege network position, or another condition defined in the engagement. The tester investigates what that access permits rather than attempting to reproduce every possible route by which an attacker could have obtained the foothold.
An internal assessment can uncover weaknesses that are difficult or impossible to see from the public internet. These may include excessive permissions, poorly protected credentials, exposed administrative services, unnecessary trust relationships, weak segmentation, or systems that become reachable only after internal access exists.
Privilege escalation means obtaining permissions beyond those available at the starting point. Lateral movement means using one foothold to reach additional systems or network locations. These concepts are often relevant to internal testing, but the engagement should validate only the paths and objectives authorized by its scope.
The test does not have a universal finish line such as obtaining administrator access. The stopping condition may instead be demonstrating access to a particular system, confirming a segmentation weakness, showing that several weaknesses can be chained, or stopping before an additional action would create unacceptable operational risk.
Authorization and Rules of Engagement Come First
Penetration testing deliberately interacts with real security controls and can include intrusive activity. Written authorization and clearly defined boundaries are therefore part of the technical assessment, not paperwork to be added afterward.
NIST defines Rules of Engagement, or ROE, as the guidelines and constraints established before a security test begins. Its Rules of Engagement definition explains that the ROE gives the test team authority to conduct defined activities without repeatedly obtaining additional permission. NIST’s template also covers scope, assumptions, limitations, risks, personnel, test schedules, and related logistical controls.
Penetration testing should be performed only with explicit authorization and within an agreed scope. Intrusive actions can disrupt production systems, so permitted techniques, excluded assets, testing windows, data-handling rules, escalation contacts, and stopping conditions should be settled before testing begins.
Operational safety is particularly important for techniques that can interrupt service. NIST notes that direct testing can produce unexpected system halts or other denial-of-service conditions and recommends considering less disruptive techniques, restricted testing windows, or suitably configured non-production systems when the potential impact is unacceptable.
Cloud environments can add provider-specific rules and shared-infrastructure considerations. Those restrictions should be checked against the provider’s current policy and the engagement’s authorization rather than assumed from general network-testing practice.
The Typical Network Pentest Lifecycle
Internal and external tests start from different positions, but both normally follow a controlled assessment process. Methodologies use different phase names, so the sequence below summarizes the common logic rather than claiming that every engagement follows identical terminology.
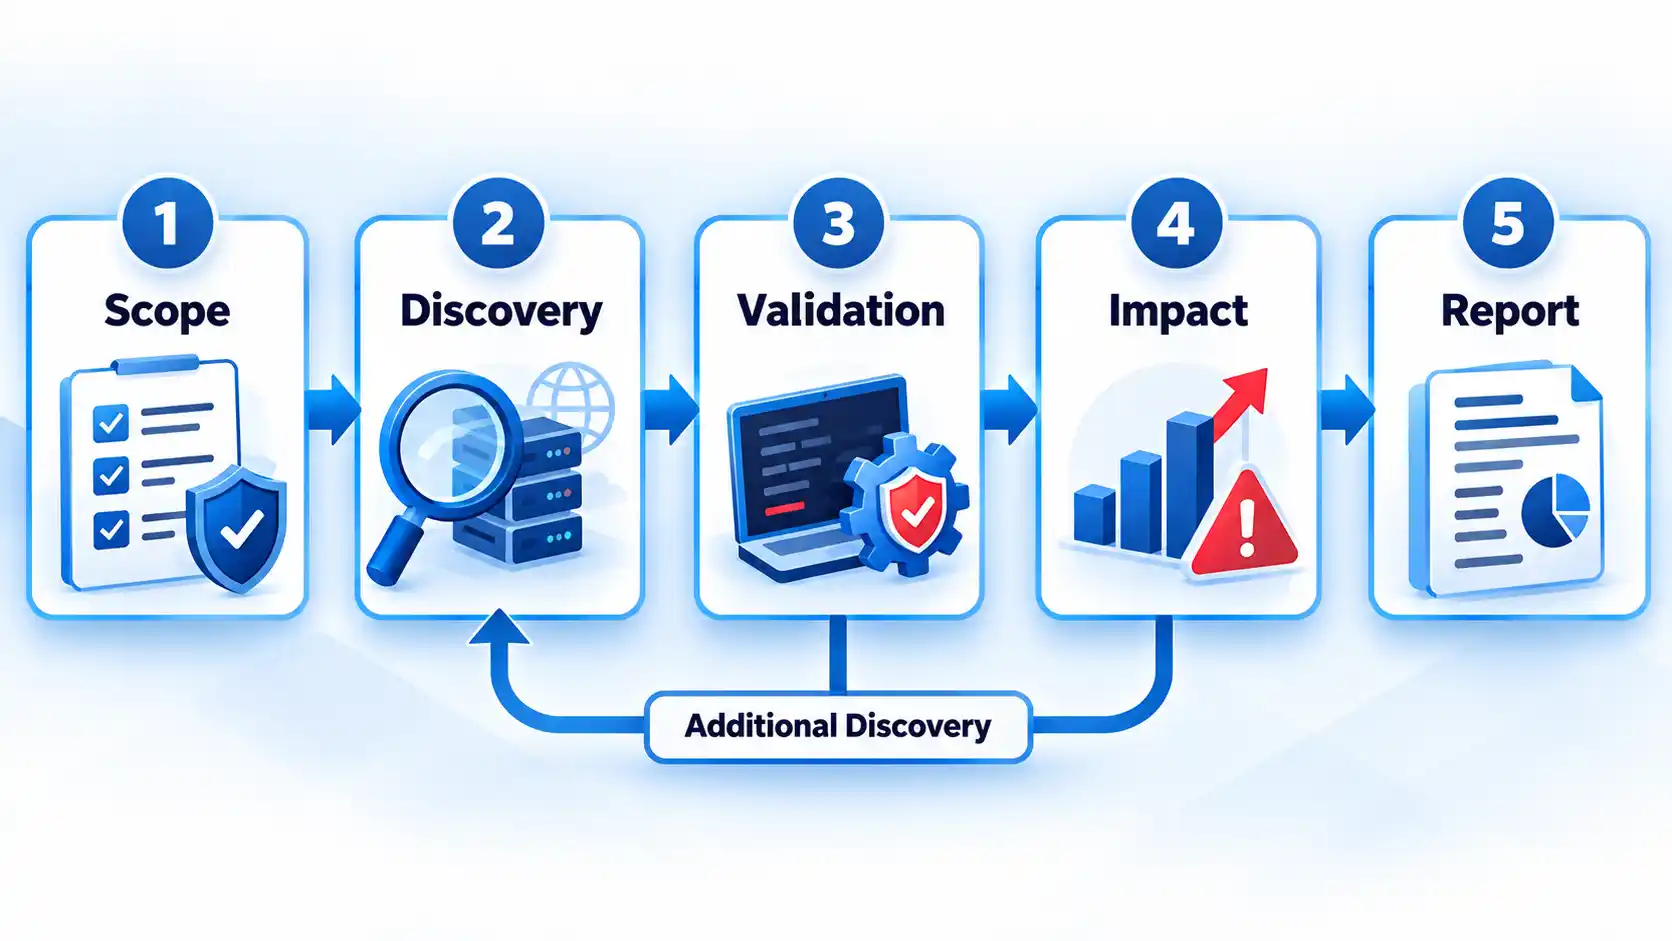
- Define the scope and Rules of Engagement. Establish the authorized assets, starting position, objectives, exclusions, permitted techniques, safety constraints, communication process, and stopping conditions.
- Discover the relevant attack surface. Identify the systems, services, exposure, and environmental information needed to understand the authorized targets from the selected internal or external viewpoint.
- Analyze potential weaknesses. Review the discovered attack surface for vulnerabilities, insecure configurations, weak controls, and plausible combinations of findings that merit validation.
- Validate selected weaknesses in a controlled manner. Determine whether important findings are genuinely exploitable without exceeding the Rules of Engagement or creating unnecessary operational risk.
- Assess authorized impact. Where permitted, determine what additional systems, privileges, network segments, or protected resources a validated weakness could expose.
- Report the evidence and remediation priorities. Document what was tested, what was demonstrated, relevant limitations, affected assets, and actions required to address the findings.
NIST presents penetration testing as an iterative process involving planning, discovery, attack or vulnerability validation, and reporting. The OWASP Web Security Testing Guide’s methodology overview also summarizes the Penetration Testing Execution Standard as seven phases: pre-engagement interactions, intelligence gathering, threat modeling, vulnerability analysis, exploitation, post-exploitation, and reporting.
A structured network penetration-testing methodology keeps discovery, validation, reporting, and retesting tied to the same agreed scope.
What These Tests Do Not Automatically Include
The labels “internal” and “external” identify testing perspectives. They do not automatically authorize every form of security testing that could overlap a broader engagement.
- Vulnerability scanning: automated scanning can support a penetration test, but scanning alone does not demonstrate the same attack-path evidence as controlled validation.
- Web application and API testing: an internet-facing application may be part of an external attack surface, but dedicated application testing can require different methods and substantially greater depth.
- Wireless testing: Wi-Fi infrastructure may be included when explicitly scoped, but it is not automatically part of every internal network test.
- Social engineering: phishing, vishing, impersonation, and other human-focused techniques require explicit authorization and their own safety boundaries.
- Physical security testing: attempting to enter facilities or physically access equipment is a separate assessment dimension unless it is specifically authorized.
- Denial-of-service testing: intentionally exhausting or destabilizing systems can create material operational risk and should not be treated as a default penetration-testing activity.
Automation also needs careful framing. Automated penetration testing can perform repeatable discovery and validation tasks, but it should not be treated as interchangeable with every human-led assessment in which unusual trust relationships, scope decisions, and environmental context may affect what requires investigation.
The boundary between network and web application penetration testing matters when an internet-facing application appears inside a broader external-network scope.
When You Need Internal, External, or Both
External Penetration Testing
Main trade-off: an external starting position can reveal perimeter exposure, but by itself it may not show the full consequences of an attacker who already has internal access.
Internal Penetration Testing
Main trade-off: starting inside the environment does not establish whether an external attacker could have obtained that foothold through the public-facing perimeter.
Both Perspectives
Main trade-off: the broader engagement requires enough time and clearly separated objectives so neither perspective is reduced to superficial coverage.
Compliance requirements can also affect scope, but they should be checked against the exact standard that applies to the organization. PCI DSS, for example, distinguishes internal from external penetration testing. PCI SSC’s published v4.0 materials describe internal testing as testing from inside the cardholder data environment and into it from trusted and untrusted internal networks, while external testing addresses the exposed external perimeter and critical systems connected to or accessible from public network infrastructure. PCI SSC’s PCI DSS v4.0.1 publication notice states that the limited revision added or deleted no requirements.
What a Useful Penetration-Test Report Should Tell You
A useful report should make clear what the assessment actually demonstrated. A long vulnerability list without scope, evidence, impact, and remediation context makes it difficult to distinguish a theoretical weakness from a path that was validated during the engagement.
The report should identify the tested scope and starting assumptions, explain the evidence behind material findings, describe demonstrated impact, identify affected systems or controls, and provide remediation guidance appropriate to the finding. The level of detail should be sufficient for technical teams to understand what needs to change without implying that every untested system was secure.
Exclusions and limitations matter as much as positive findings. An asset that was outside scope, unavailable during testing, or protected by a restriction in the Rules of Engagement should not silently appear equivalent to an asset that was fully assessed and produced no finding.
Retesting can confirm whether remediation closed the demonstrated weakness. PCI DSS Requirement 11.4.4, for example, requires exploitable vulnerabilities and security weaknesses identified through penetration testing to be corrected according to the entity’s risk assessment and penetration testing to be repeated to verify the corrections. Organizations outside PCI DSS can still apply the same practical principle when retesting is part of their engagement: a fix is more useful when the previously demonstrated path can no longer be reproduced.
External and internal penetration testing provide different views of the same defensive problem. External testing examines exposure from outside the trusted environment, while internal testing examines what can happen after a foothold already exists. The appropriate scope depends on the question the organization needs the assessment to answer.

💬 Comments